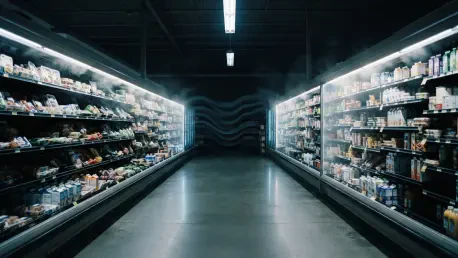
Coordinated attacks on Swedish grocery chains have revealed that many industrial monitoring connections fail to meet basic security and insurance requirements. Imagine a shopper entering a local supermarket, expecting the brisk chill of the frozen goods aisle, only to be met with the smell of thawing produce and the sight of condensation dripping from glass doors. This scenario became a reality for several major retail locations in Northern Europe. In early November, hackers managed to infiltrate the cooling controllers of various ICA and Coop locations, remotely overriding standard operating procedures. By manipulating the internal settings, these unauthorized actors successfully raised the temperatures in industrial freezers to a staggering 55 degrees Celsius. Instead of preserving perishables, the refrigeration units were effectively transformed into ovens. This unprecedented breach forced immediate store closures as staff struggled to manage the resulting food spoilage and equipment failures.
Identifying the Entry Points: The IoT Security Gap
The investigation into these incidents points toward a recurring theme in the realm of specialized Internet of Things hardware: the inherent vulnerability of devices connected directly to the public internet. While the Swedish retail giant ICA confirmed that the specific breaches occurred through external connections rather than their internal corporate network, the exact software flaws utilized are still being analyzed by cybersecurity forensic teams. This situation closely mirrors a wave of similar digital interference recently documented across France. In those instances, the French national cyber response team, known as CERT-FR, discovered that attackers specifically targeted exposed management interfaces on industrial controllers manufactured by prominent brands like Danfoss and Copeland. These devices, often left with default configurations, provide a direct pathway for malicious actors to bypass traditional security perimeters and gain administrative control over critical physical systems.
Attackers have demonstrated a sophisticated understanding of industrial refrigeration logic, specifically by exploiting the defrost mode intended for routine maintenance. By forcing these units into a continuous heating cycle, hackers can generate significant thermal energy within a space designed for sub-zero temperatures. This method is particularly insidious because it utilizes the machine’s own hardware functions to cause damage, rather than relying on external code execution. The shift in tactics suggests that cybercriminals are moving away from traditional data exfiltration or financial record theft, focusing instead on the disruption of physical infrastructure. This evolution in the threat landscape highlights a critical oversight in how operational technology is managed. Many businesses have failed to segregate their industrial control systems from standard web traffic, leaving essential equipment like compressors and cooling fans susceptible to remote manipulation.
Mitigating Risks: Strategic Defense for Cold Chains
To combat this rising threat, cybersecurity experts recommend an immediate and multi-layered defense strategy that prioritizes the isolation of industrial hardware. One of the most effective steps involves removing cooling controllers from the public internet entirely and requiring the use of secure Virtual Private Networks for any necessary remote access. This simple architectural change prevents automated bots and opportunistic hackers from identifying vulnerable interfaces through common search engines. Furthermore, maintaining up-to-date firmware is essential, as manufacturers frequently release patches to address the very vulnerabilities exploited in these attacks. Simply resetting the hardware after a breach is often insufficient; without a fundamental change in network exposure, systems are likely to be re-infected within minutes of going back online. Establishing a protocol for immediate password changes and the implementation of multi-factor authentication can further protect vital cooling systems.
Retailers and logistics providers took proactive steps to coordinate more closely with their refrigeration specialists to ensure that all monitoring connections were fully compliant with modern insurance mandates. This shift in operational strategy recognized that securing the food supply chain required more than just physical locks; it demanded a robust digital fortress. By integrating operational technology into the broader cybersecurity framework, organizations moved toward a model of continuous monitoring and rapid response. The lessons learned from the Swedish and French incidents emphasized the importance of visibility across all connected assets. Ultimately, the transition toward air-gapped or heavily encrypted control systems provided a blueprint for protecting physical infrastructure from digital sabotage. These measures not only prevented future disruptions but also ensured that the technology designed to keep food fresh remained reliable. The industry eventually adopted a culture of security by design to protect hardware.