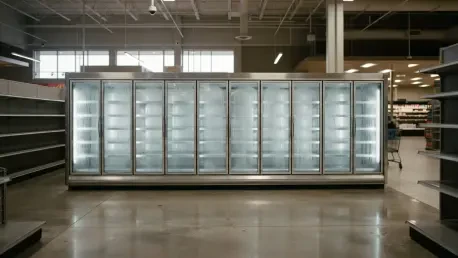
The transition from digital data breaches to kinetic-effect cyberattacks represents a dangerous new trend in the targeting of essential civilian infrastructure. In mid-October, specifically on the 11th and 12th, the world witnessed a sobering manifestation of this threat as refrigeration units across France’s largest supermarket chains began to fail simultaneously. Unlike typical ransomware attacks that aim for financial extortion or data theft, these incidents targeted the physical operational integrity of industrial cooling systems. This coordinated campaign led to the mass spoilage of temperature-sensitive food supplies and, more alarmingly, triggered at least fifteen documented fires within retail spaces. By manipulating hardware safety thresholds remotely, the attackers demonstrated that the boundary between the digital and physical worlds has become dangerously porous. This incident, now at the center of a major geopolitical storm, signals a shift where the tools of cyber warfare are used to disrupt the most basic necessities of civilian life.
Technical Execution: Impact on Infrastructure
The Mechanics: Understanding the Breach
Technical forensics revealed that approximately 700 retail locations were hit by a sophisticated override of their Industrial Control Systems (ICS). The attackers did not simply shut down the power; they systematically accessed the temperature regulation software and bypassed standard safety protocols designed to prevent overheating. By forcing industrial compressors to operate at maximum capacity while simultaneously raising the ambient set-points to 50 degrees Celsius, or 122 degrees Fahrenheit, the hackers pushed the equipment far beyond its intended operational range. This methodology required a deep understanding of the proprietary logic used in commercial refrigeration hardware, suggesting a high level of preparation and specialized intelligence. The result was a catastrophic failure of the cooling cycle that rendered thousands of tons of perishable goods unsafe for human consumption within hours of the initial breach.
Specialized Units: The Shahed Kaveh Connection
Investigators from the French national cybersecurity agency identified specific code signatures and command-and-control infrastructure linked to the Shahed Kaveh unit, a specialized cyber arm of the Islamic Revolutionary Guard Corps (IRGC). This attribution was supported by the discovery of digital footprints that mirrored previous operations attributed to Iranian state-sponsored actors targeting water and energy sectors. The precision of the French refrigerator attacks suggests that the perpetrators spent months mapping the network architecture of the targeted supermarket chains. By exploiting vulnerabilities in remote management interfaces—often left exposed for the convenience of third-party maintenance contractors—the attackers gained the lateral movement necessary to infect hundreds of localized controllers from a single point of entry. This level of synchronization points to a state-level operation rather than a decentralized group of hacktivists.
Public Safety: Risks and Infrastructure
Physical Consequences: Fires and Failures
The consequences of these attacks extended beyond mere financial losses for the retailers, as the extreme thermal stress placed on the compromised equipment posed a significant risk to human life. In at least fifteen separate instances, the forced overheating of refrigeration motors led to electrical short circuits and the ignition of insulation materials, resulting in actual fires that required emergency fire department intervention. These were not accidental failures but the direct result of a kinetic-effect strategy designed to cause physical destruction through digital means. The fact that these fires occurred in public spaces during business hours added a layer of psychological terror to the incident, as shoppers and employees were forced to evacuate smoking buildings. This shift from disrupting service to endangering lives marks a crossing of a red line in the norms of international engagement, prompting French officials to treat the matter with the same gravity as a traditional physical assault.
Systemic Weakness: The Vulnerable Internet of Things
This event has highlighted a systemic vulnerability inherent in the rapid adoption of Internet of Things (IoT) technology across European infrastructure. While connecting cooling systems to the internet allows for efficient monitoring and energy management, it also creates an expansive attack surface for hostile actors. Reports from the European Union Agency for Cybersecurity (ENISA) indicate that similar, albeit smaller, anomalies have been detected in eleven other countries, suggesting a broad probe of the continent’s food supply chain resilience. Experts now warn that any internet-connected device, from a thermostat to a massive industrial freezer, serves as a potential gateway for state-sponsored actors to bypass traditional border defenses. The consensus among security analysts is that the digitization of the supply chain has outpaced the implementation of robust security frameworks, leaving essential services exposed to actors who view civilian disruption as a legitimate tool of statecraft.
Diplomatic Fallout: International Reactions
The Strategy: European Union Sanctions
French Foreign Minister Jean-Noël Barrot took the unprecedented step of formally publicizing the government’s findings on November 9, explicitly naming the IRGC as the orchestrator. This was followed by the immediate summoning of the Iranian ambassador to the Quai d’Orsay, where French diplomats delivered a stern condemnation of the attacks. Paris is now actively lobbying its European partners to implement a coordinated sanctions regime that targets the individuals and entities involved in the Shahed Kaveh unit. By framing these cyber-physical attacks as a direct violation of international law and a threat to European food security, France aims to build a consensus for a more aggressive posture toward Tehran. The goal is to move beyond simple diplomatic protests and establish a precedent where digital aggression against civilian infrastructure carries tangible economic and political costs for the responsible nation-state.
Verification Issues: The European Split
The push for unified sanctions has met with varying degrees of enthusiasm among other European Union members, revealing significant fractures in how the bloc handles cyber attribution. In Belgium, for instance, a notable divide emerged between top government officials regarding the appropriate response to the French findings. Interior Minister Bernard Quintin described the link to Iran as highly probable based on shared intelligence, yet Foreign Minister Maxime Prévot argued that the evidence presented was still too circumstantial to justify the legal threshold required for sovereign sanctions. This internal friction reflects a broader challenge within the EU, where different nations have different standards for what constitutes irrefutable proof in the digital realm. Without a unified forensic standard, the ability of the Union to project a strong, collective front against state-sponsored cyber threats remains hampered by procedural and political caution.
Geopolitical Context: The Iranian Response
Tehran’s Rebuttal: Claims of False Flags
Tehran’s response to the allegations has been one of categorical denial, with officials characterizing the French claims as a false flag operation designed for political gain. Brigadier General Mohebi of the IRGC issued a statement suggesting that the technical evidence was fabricated by Israeli intelligence to fuel a narrative of Iranophobia across Europe. He maintained that Iran’s military and cyber doctrine strictly prohibits the targeting of civilian businesses and essential services, contrasting this with the actions of Iran’s regional adversaries. Meanwhile, Foreign Minister Abbas Araghchi argued that the French government is utilizing the cooling system crisis as a convenient diversion from its own internal political instability and widespread domestic protests. By linking the accusations to the broader geopolitical climate, Tehran is attempting to portray the French stance as a hypocritical maneuver intended to isolate Iran during a period of high regional tension.
Future Security: Addressing Network Vulnerabilities
The resolution of the refrigerator crisis required immediate structural changes to how industrial equipment is secured and monitored across the continent. Moving forward, the incident established a clear precedent for the secure-by-design philosophy, where manufacturers integrated hardened security protocols into the hardware layer rather than treating software updates as an afterthought. From 2026 to 2028, the implementation of mandatory auditing for all internet-connected industrial assets became a central pillar of European security policy. Security experts recommended that companies strictly segregate their operational technology from their corporate networks to prevent the lateral movement seen in the French attacks. Ultimately, the crisis proved that the safety of a nation’s food supply is no longer just a matter of logistics, but a critical component of its digital defense strategy. These actions ensured that the vulnerabilities exploited during the cooling system breach were systematically closed, reinforcing the resilience of civilian networks.